A case study on CVE-2026-82533 (DeepSeek Harness) and four related 2026 AI-agent sandbox escapes across OpenAI Codex, Cursor, and Docker Sandboxes: the sandbox denied file writes exactly as designed, and nobody designed anything to stop a request to the control panel sitting right next to it. Includes an original, kernel-enforced OS-level reproduction with full screenshots.
A complete security teardown of a babyagi-based researcher / writer / editor pipeline: twelve framework-level findings, forty-nine attack vectors across ten groups (35 verified live in running code), the exact command and real transcript behind every runnable exploit, and a working before/after patch for a correct authorization check that quietly leaked its secret scope one bit per question.
A plain-English introduction to the delegation problem in agentic AI: ghost permissions, scope drift, and broken audit trails, walked through with a real case study, a deliberate indirect-injection attack chain, a STRIDE trust-boundary view, and a half-life-of-accountable-delegation model comparing opaque, attenuated, and attested governance postures.
Audit-ready LLM threat coverage atlas with 500 mapped vectors, OWASP/MITRE/NIST/governance crosswalks, architecture filters, per-leaf review notes, an AI offensive pentest checklist, and JSON/CSV exports. It is a review surface, not a completeness score.
A visual companion to the LLM Threat Coverage Atlas: the full attack-vector checklist regrouped into clustered domains as an interactive bubble map, with the quorum/approval cluster called out.

A brand-new twelve-part mini series on the one primitive every multi-agent framework shares — the handoff — and the twelve ways it breaks. An offline, runnable lab with a VULN/DETECT/FIXED policy switch, a STRIDE slice per exploit, and the measured result that an input filter tops out at 43% where structural controls reach 100%. All twelve parts (A1–A12) are live.

An LLM-agent privilege-escalation incident walked step by step: the agentic loop, the trust boundary, indirect prompt injection, proof of concept, detection, and defense-in-depth remediation.
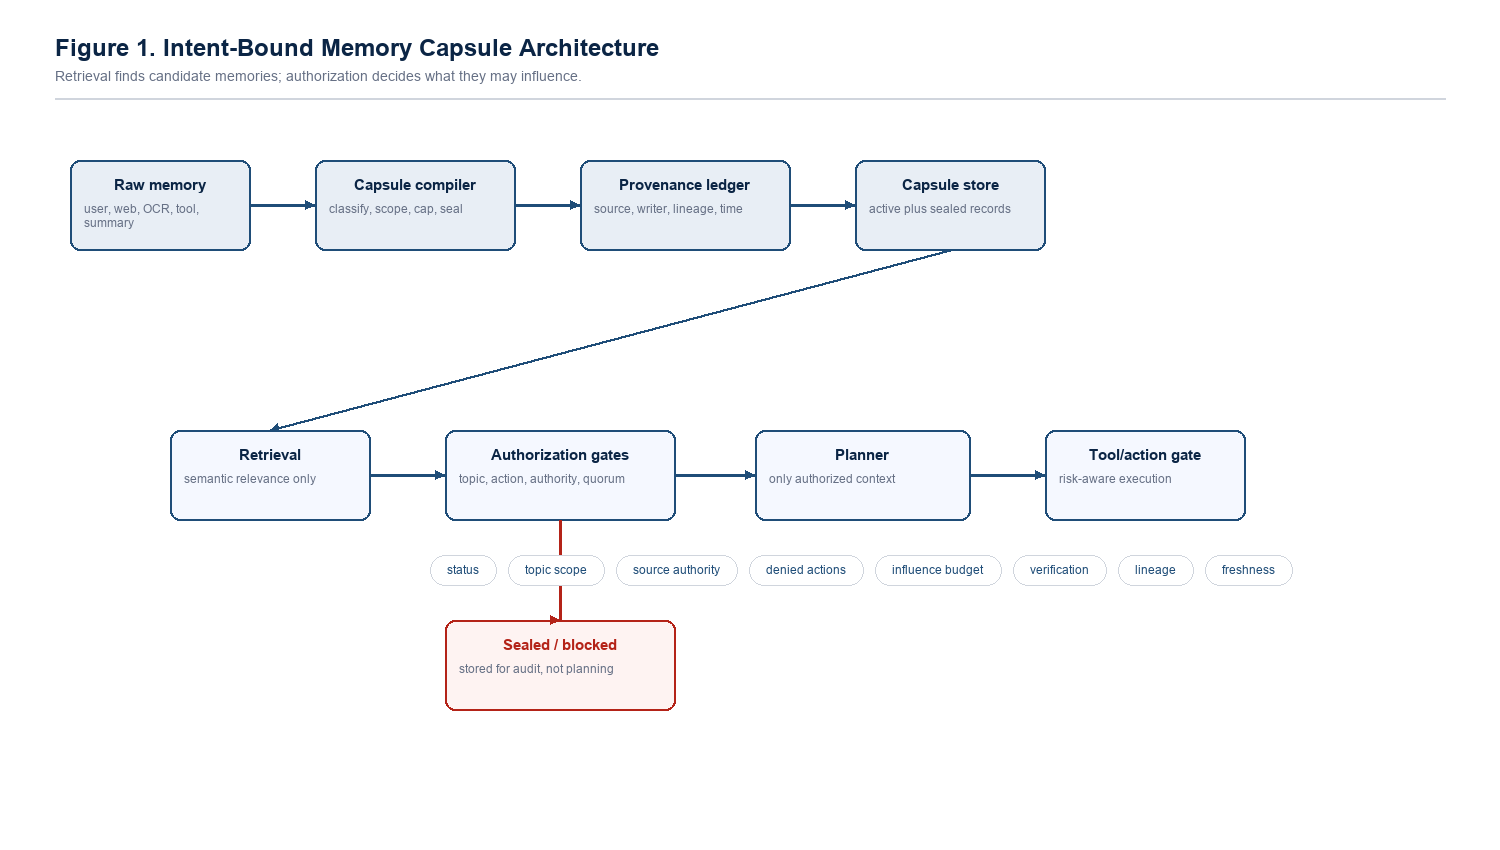
A research companion for CapsuleGuard: why LLM-agent memory retrieval is not authorization, how intent-bound capsules block poisoned planning influence, and what the v3 paper evidence actually proves.
The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this sit...
The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this sit...

The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this sit...

The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this sit...

The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this sit...

The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this site
The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this site
The information provided in this site is for educational purposes regarding pentesting. The author of the site will not be held any responsibility for any misuse of the information from this site